Nothing improvises on your endpoints.
Every fix Nanoheal runs is validated, versioned and sealed, so it runs the same way every time. You decide what runs silently, what needs a click and what waits for an approval.

Windows 11 24H2 · approved by A. Chen
- Pilot · 50 devicesDone
49 installed · 1 failed and rolled back automatically
- Ring 1 · 1,200 devices64%
768 installed · 0 failed · 432 pending
- Estate · 17,170 devicesNeeds approval
Reviewed. Staged. Logged. Reversible.
Every fix passes the same gates before it reaches your devices.
-
Reviewed
Capabilities reach endpoints through staged, approved and versioned publishing. Nothing goes live until a person signs it off.
-
Staged
Publish to a pilot group, check the result, then widen the rollout.
-
Logged
The audit log shows who changed what, who approved it and where it ran.
-
Reversible
Nanoheal handles software distribution and patch install with rollback, so a bad update can be undone.
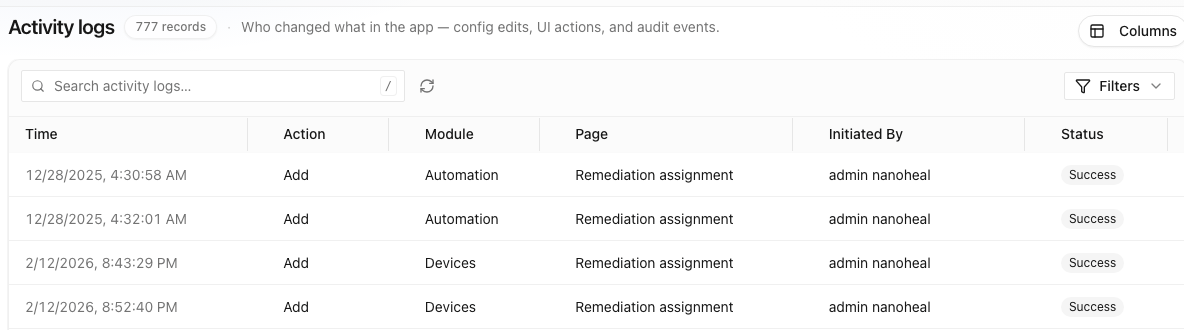
Activity logsWho changed what in the app
| Time | Change | By | Status |
|---|---|---|---|
| 12/28/2025, 4:30:58 AM | Add · Automation | admin nanoheal | Success |
| 12/28/2025, 4:32:01 AM | Add · Automation | admin nanoheal | Success |
| 2/12/2026, 8:43:29 PM | Add · Devices | admin nanoheal | Success |
| 2/12/2026, 8:52:40 PM | Add · Devices | admin nanoheal | Success |
Controls that ship in the product today.
Who can do what
| Create a capability | Approve | Run on a group | Roll back | Read the log | |
|---|---|---|---|---|---|
| Author | |||||
| Approver | |||||
| Operator | |||||
| Auditor |
- Access
- Role-based access, checked on every capability. Users act only where their role and sites allow.
- Sign-in
- Time-based one-time password MFA with backup codes for console users, plus SAML and OIDC single sign-on configured per site.
- Tenancy
- Each customer or business unit is a site, with data scoped to each site, with requests for another site refused.
- Secrets
- Passwords are hashed, with secret fields stripped from responses and redacted from logs.
- API access
- Site-scoped API keys, stored only as hashes, each limited to read or write.
- Device identity
- Mutual TLS between agent and server, with certificates admins can list and revoke.
ComplianceSOC 2 Type ISOC 2 Type II in progressGDPRThe SOC 2 Type I report is available on request. Request the report
Where your data lives, and how long we keep it.
What we collect. Endpoint and experience telemetry, for monitoring, analytics and fixes. Visibility, anonymisation and retention follow your configuration, and Haya applies PII masking to declared personal fields. Field-level detail is shared through our security review.
Where it lives. The SaaS runs on AWS by default, or Azure or GCP, in the region set for your deployment; on-premises and air-gapped deployments are designed with your team. On request: a DPA with the sub-processor list, and our VPAT.
- 01 · On the deviceCollected
Endpoint and experience telemetry. Visibility and anonymisation follow your configuration.
- 02 · On the wireSent
Mutual TLS between agent and server.
- 03 · At restStored
In the region set for your deployment: SaaS on AWS by default, Azure or GCP, on-premises or air-gapped.
- 04 · AfterKept, then deleted
As agreed with you, to fit your deployment and contract.
The intelligence proposes. A person validates. The device runs the validated version.
If it changes a device, a person approved it and the log can show it.
- 01The intelligence proposes HRebuild the Outlook OST on 212 devicesCrashes up 4× since Tuesday’s update
- 02A person validates AKApproved by IT lead10:14 · Rebuild OST v3Publish
- 03The device runs the validated version Running on 212 devices209 succeeded · 3 retrying
Audit logEvery step above, with who did it and when.
Haya, Nanoheal’s AI and analytics, spots anomalies against each device’s own history, forecasts trouble, finds where it came from and proposes the fix. It cannot change a device. Fixes reach devices only through the same approval and publishing path as everything else on this page. Once a person approves a fix, it runs on its own wherever it applies, and every run is logged.
Haya itself runs with approval gates, role-based access, execution traces and PII masking, on your choice of model, including a locally hosted one.